Compliance · Specification readiness review
Review requirements with context.
Check your spec against enabled frameworks. Review evidence and recommendations; this is not a certification.
Plan and usage limits apply. View pricing
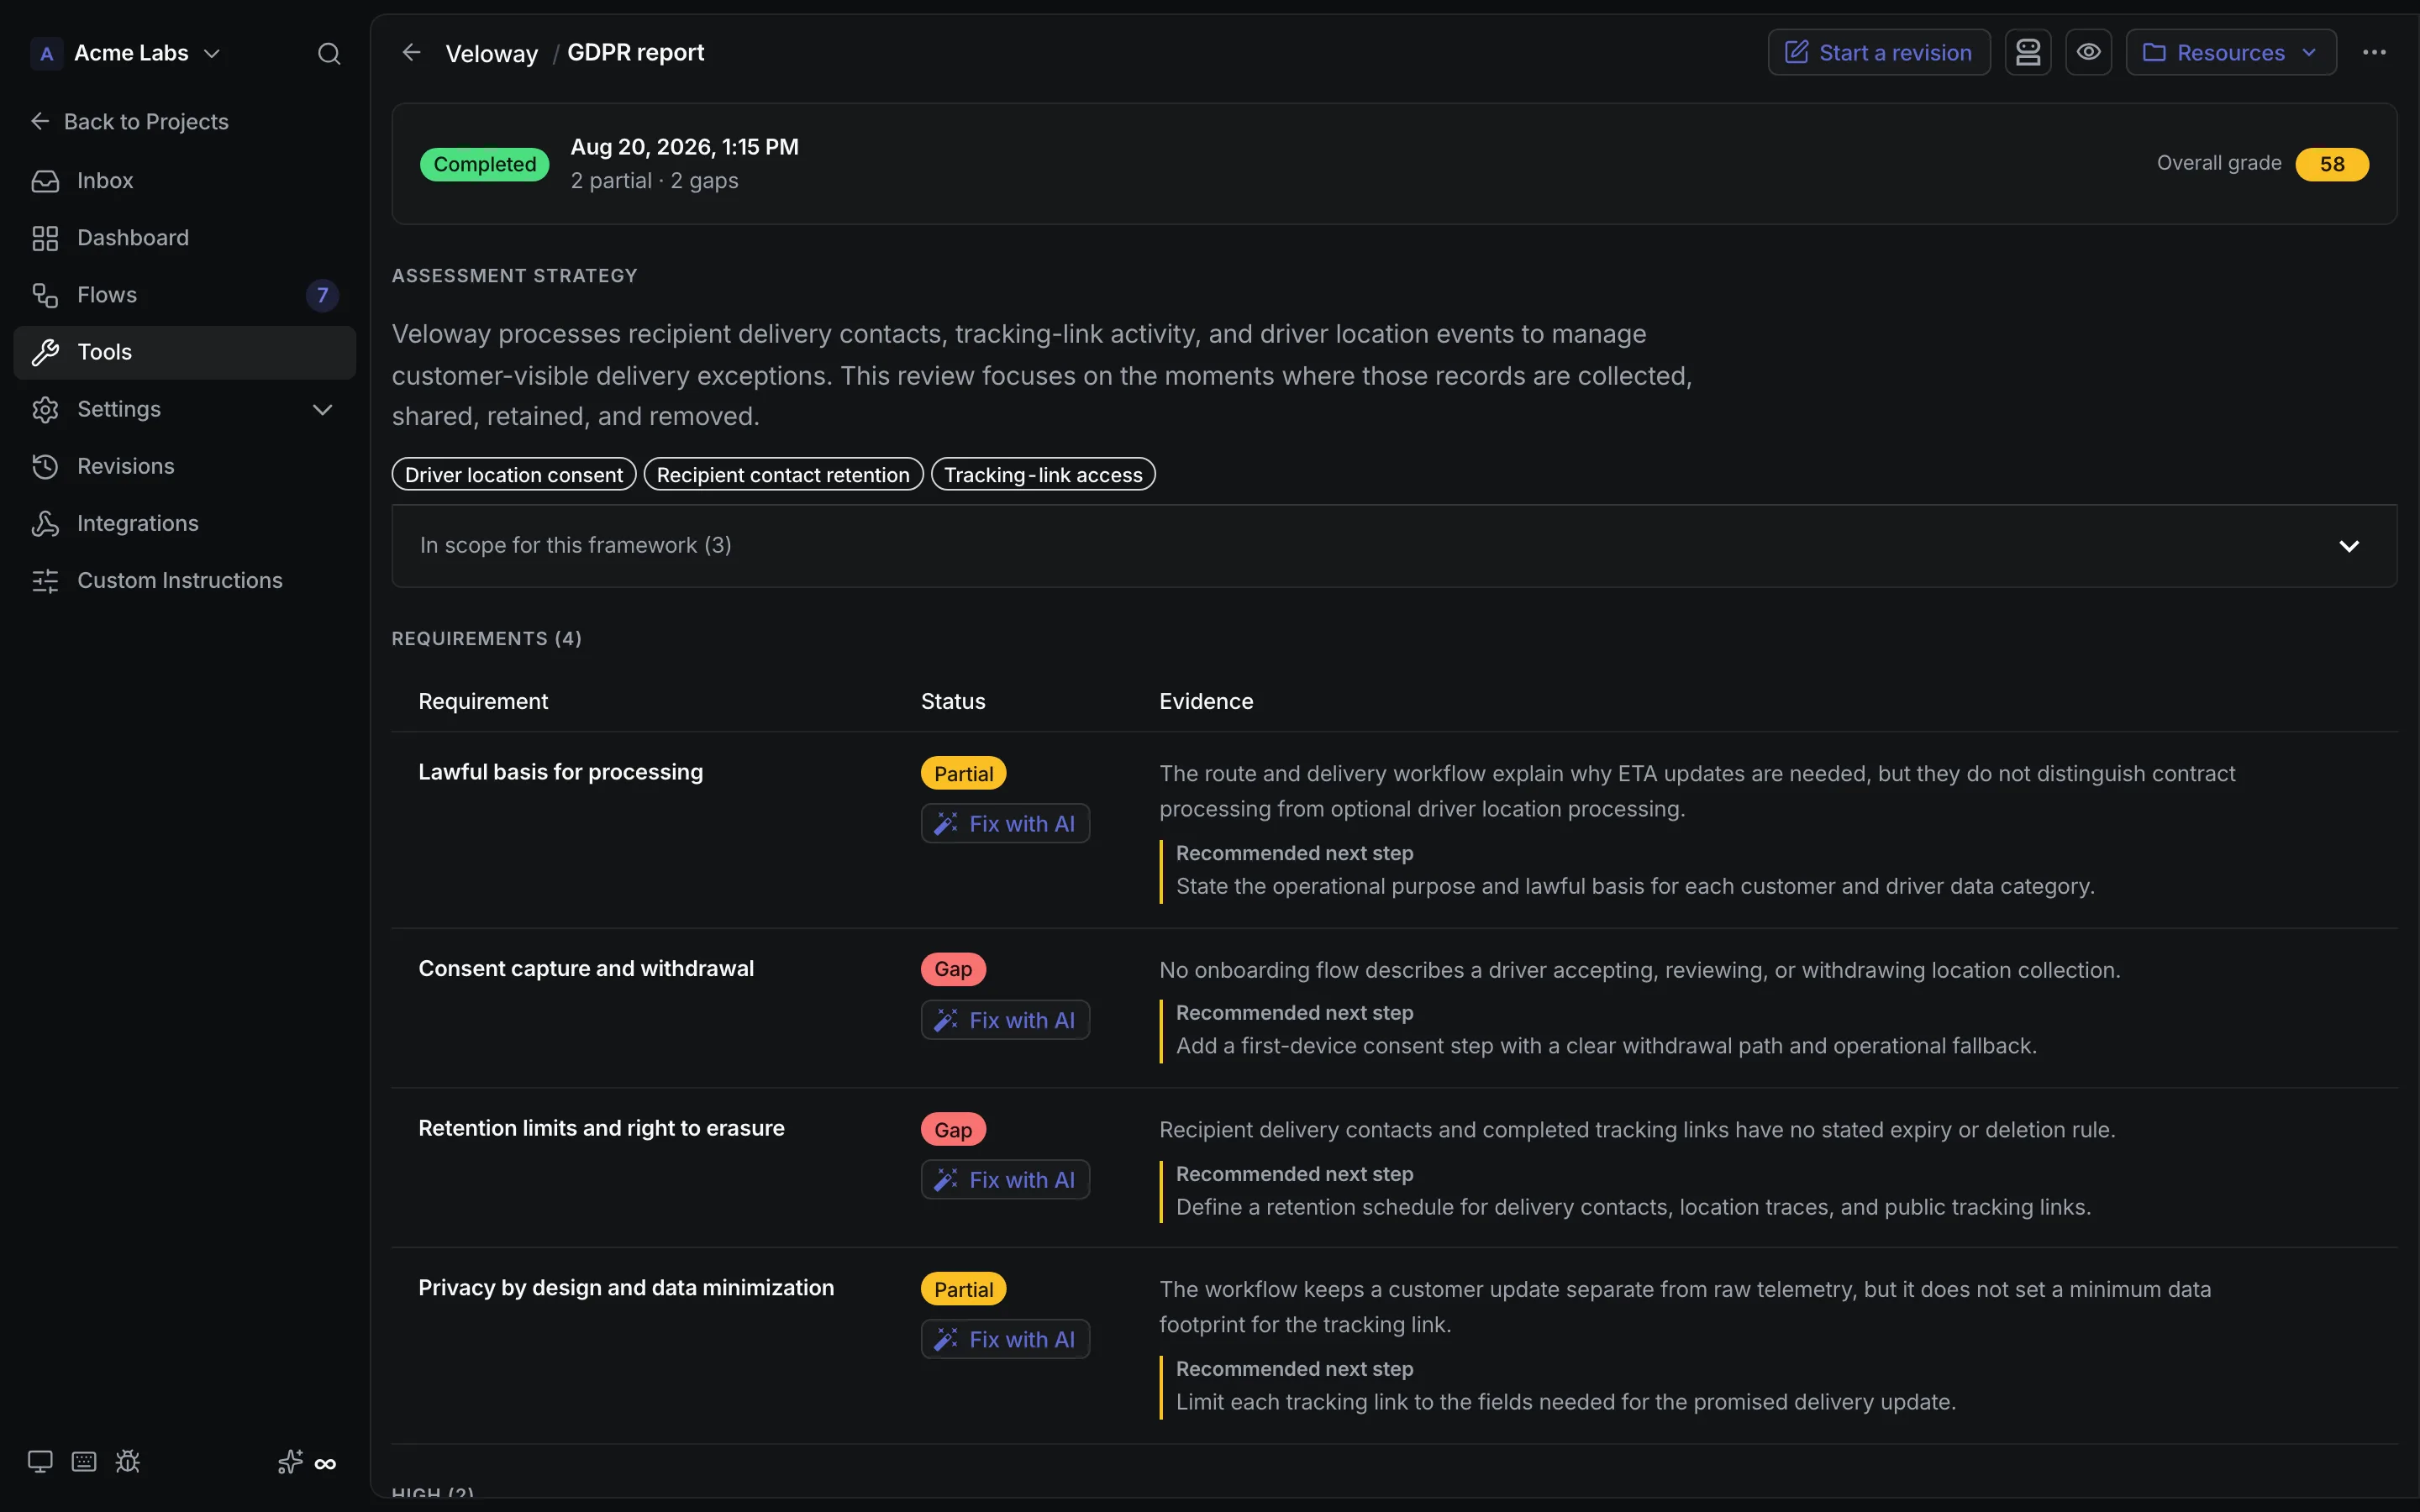
Product walkthrough
Compliance, in context.
Demo project data shown for illustration.
Screen 01 / 03
GDPR delivery-data review
A GDPR review grounded in delivery data
A closer look
The details,
when you need them.
Explore the workflow, what it produces, and how access works.
How Compliance works
Compliance checks the current project specification against the frameworks a team enables, producing a requirement-level report with evidence and recommendations.
- An owner or admin enables the relevant built-in frameworks for the project.
- Run a check and follow its progress into a dedicated, persisted report.
- Review the strategy, in-scope entities, requirement matrix, severity-grouped findings, and AI fix handoffs.
A practical example
A product owner wants to understand where a new health-data workflow has gaps against the team’s enabled requirements and who needs to resolve each one.
What you get
A requirement-level review record
- Scores or N/A results for enabled framework checks
- Spec-grounded evidence, recommendations, and handling state for each finding
- Immutable saved reports that stay readable as the framework catalog evolves
Using Compliance
This is a specification review tool, not a certification or a substitute for legal, security, or compliance advice. Framework enablement is project-specific and managed by owners or admins.
Keep exploring